Skip to content
System OnlineLayyah, Pakistan · PKT · UTC+5

AI Security Engineer & AI/ML Security Researcher. I build intelligent systems that detect and understand threats — and I adversarially test the AI everyone is rushing to deploy.

Muhammad Taha — AI Security Engineer
SYSTEM STATUSLIVE
  •  ACTIVE
  •  ACTIVE
  •  ACTIVE
  •  ACTIVE
  •  MONITORING
01 / About

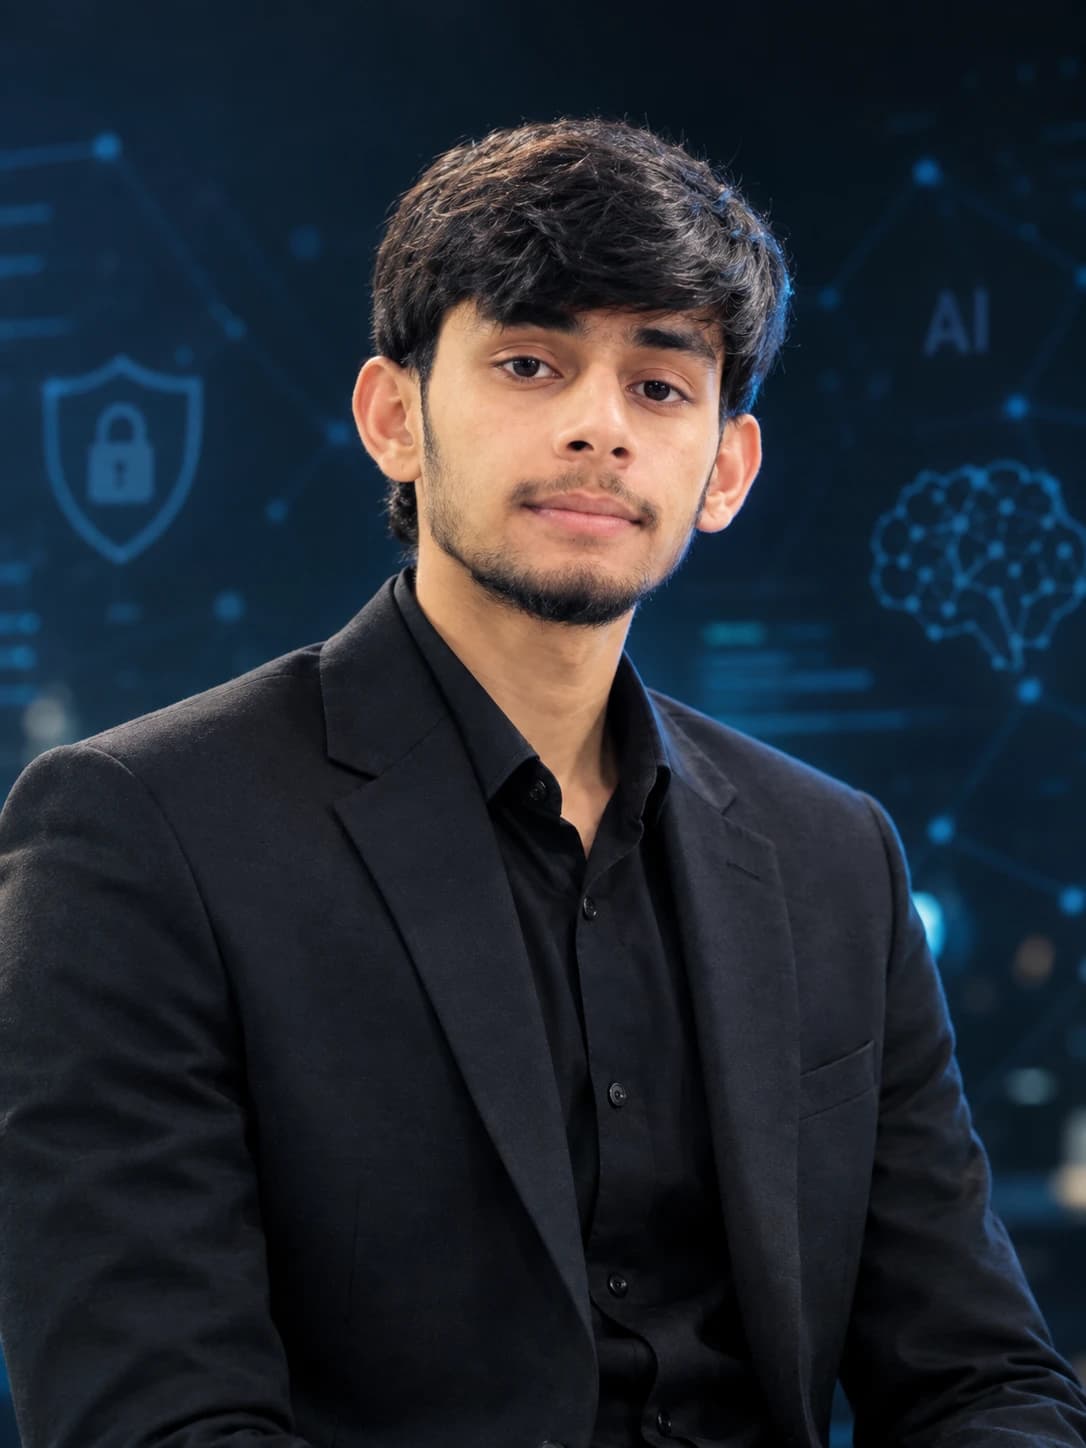
Portrait of Muhammad Taha
EDUCATION
BSc Computer Science
GRADUATING
2028
BASED IN
Layyah, PK
LANGUAGES
EN · UR

I build and break intelligent systems.

I'm an AI Security Engineer and AI/ML Security Researcher focused on the point where machine learning meets the threat model. My work sits across two fronts: engineering systems that detect and understand attacks, and adversarially testing the AI systems everyone is racing to deploy.

I care about the parts most people skip — how a model fails under a crafted input, how a prompt slips past a guardrail, how an alert pipeline behaves at 3am when it actually matters. I approach security as an engineering discipline: reproducible, measured, and built to hold up under pressure.

I'm currently studying Computer Science at UET Taxila while building a portfolio of security engineering and AI red-teaming work — driven less by credentials and more by the questions I keep wanting to answer.

FOCUS AREAS
AI SecurityLLM / GenAI SecurityAI Red TeamingAdversarial Machine Learning
02 / Capabilities

Organized by domain rather than dumped as a list — from AI security down to the systems it runs on.

AI Security

PRIMARY
LLM SecurityAI Red TeamingPrompt InjectionAdversarial MLData Leakage TestingModel Robustness

AI / ML

06
Machine LearningDeep LearningPyTorchAnomaly DetectionLLMsRAG

Cybersecurity

06
Network SecurityCryptographySecurity MonitoringThreat DetectionMalware AnalysisSecurity Engineering

Systems & Networking

05
Operating SystemsComputer NetworksLinuxDatabasesData Structures & Algorithms

Languages

03
PythonCC++

Tools & Infrastructure

04
DockerGit / GitHubAPIsCloud / Deployment
03 / Projects

A roadmap of AI-security and ML systems in active development. Each is framed by what it's designed to do — repositories and demos go live as they ship.

01 · Flagship

AI-Powered SOC Analyst

An analyst that reads the logs first.

BUILDING

A security operations assistant that ingests logs, classifies threats with machine learning, and guides investigation — prioritizing what matters and surfacing recommendations to a human analyst.

ARCHITECTURE
IngestEnrichClassifyPrioritizeRecommend
CAPABILITIES
  • Security log ingestion
  • ML-based threat classification
  • AI-assisted investigation
  • Alert prioritization
  • Security recommendations
  • Analyst dashboard
STACK
PythonPyTorchML ClassificationLLMsDocker
Repo soon Demo soon
02 · Flagship

ML Network Intrusion Detection System

Anomalies in traffic, before they become incidents.

BUILDING

A network intrusion detection system that analyzes traffic, extracts features, and uses multiple ML models to detect anomalies and classify attacks — with an evaluation harness to compare model performance.

ARCHITECTURE
CaptureExtractModelDetectAlert
CAPABILITIES
  • Network traffic analysis
  • Feature extraction
  • Anomaly detection
  • Attack classification
  • Multiple ML models
  • Performance evaluation
STACK
PythonPyTorchAnomaly DetectionFeature Engineering
Repo soon Demo soon
03 · Flagship

AI Red-Team / AI Security Testing Platform

Adversarial pressure-testing for AI applications.

BUILDING

A platform for evaluating the security of AI systems — running prompt-injection and adversarial tests, probing for data leakage, and generating automated security reports on an application’s AI attack surface.

ARCHITECTURE
TargetProbeEvaluateScoreReport
CAPABILITIES
  • Prompt injection testing
  • AI security evaluation
  • Data leakage testing
  • Adversarial testing
  • Automated security reports
  • AI app security assessment
STACK
PythonLLMsRAGAdversarial MLAPIs
Repo soon Demo soon

Malware Analysis Assistant

BUILDING

Static, dynamic, and ML-assisted triage.

An analysis assistant that combines static and sandbox-based behavioral analysis with file and hash inspection, extracting features and applying ML to assist classification — then compiling security reports.

PythonML ClassificationSandboxingDocker
Repo soon Demo soon

Adversarial ML Research Project

BUILDING

Attack, defend, measure, repeat.

A research project studying adversarial examples and model robustness — running attack/defense experiments, evaluating security under crafted inputs, and documenting findings.

PythonPyTorchAdversarial MLResearch
Repo soon Demo soon
04 / Research

A working log of security research and experimentation — not a publication list. This is where I test ideas about how AI systems fail and how to make them harder to break.

THREAD 01

Adversarial robustness

Studying how models behave under crafted inputs, and what defenses actually hold up versus what only looks good on a benchmark.

Adversarial MLRobustness
THREAD 02

LLM & GenAI security

Exploring prompt injection, jailbreaks, and data-leakage paths in LLM applications, and how to evaluate them systematically.

LLM SecurityRed Teaming
THREAD 03

ML for defense

Applying anomaly detection and classification to security telemetry — intrusion detection, log triage, and malware analysis.

Threat DetectionAnomaly Detection

// No papers or preprints yet — this section grows with the work.

05 / Activity

Live contribution activity from GitHub — the day-to-day of learning and shipping.

06 / Contact
Open to AI Security internships

Let's build something secure.

Open to AI security and cybersecurity internships, research collaboration, and interesting problems at the intersection of ML and security. The fastest way to reach me is email.